
The Department of Health cybersecurity standard
What ADHICS asks of an Abu Dhabi healthcare entity
Every healthcare entity licensed by the Department of Health in Abu Dhabi answers to it under ADHICS for health information and cybersecurity. We confirm your tier, map the controls that apply to one control set and keep the evidence ready for your next audit.
Get ready for your ADHICS review
The health information and cybersecurity controls DOH audits
ADHICS protects Abu Dhabi's healthcare ecosystem.
The Abu Dhabi Health Information and Cyber Security Standard is DOH's cybersecurity framework for healthcare. ADHICS applies to every healthcare entity in Abu Dhabi, hospitals, clinics, pharmacies, laboratories, and healthcare IT vendors. The standard covers governance, risk management, asset management, access control, data protection, incident response, and business continuity. DOH checks ADHICS through assessments and audits, and expects incidents to be reported to it within 24 hours.
One control set for the ADHICS controls that apply to your tier.
Establish Information Security Governance
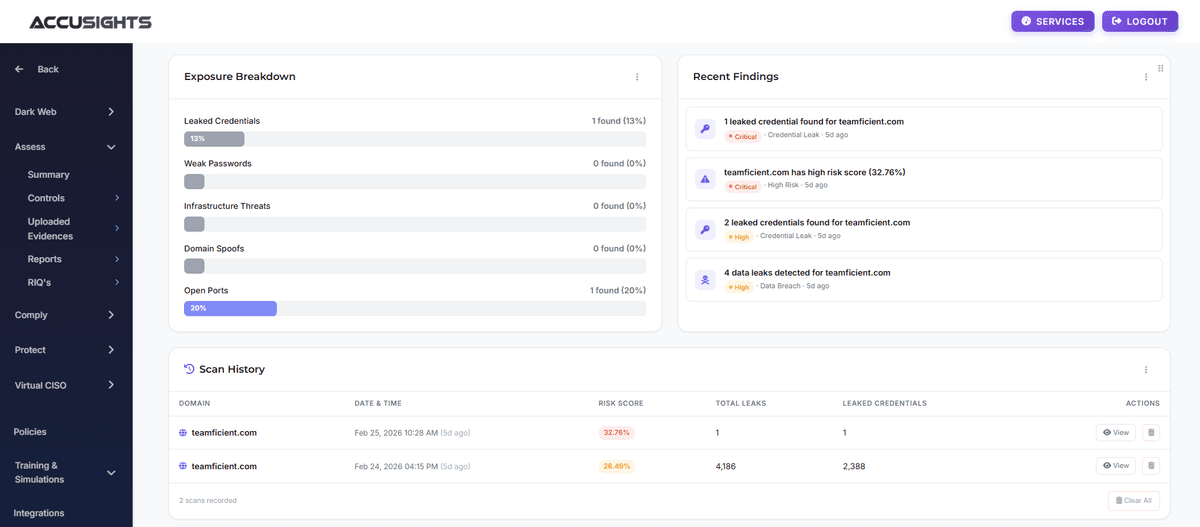
ADHICS requires formal information security governance: policies, procedures, roles, responsibilities, and oversight structures. We map the ADHICS governance requirements, assess whether your policies, roles and oversight structures exist, assign remediation and keep the governance documentation DOH auditors check. Approving policies and naming roles stay with your entity.
Governance requirements mapped, with an owner for each policy and role.
Implement Risk Management and Assessment
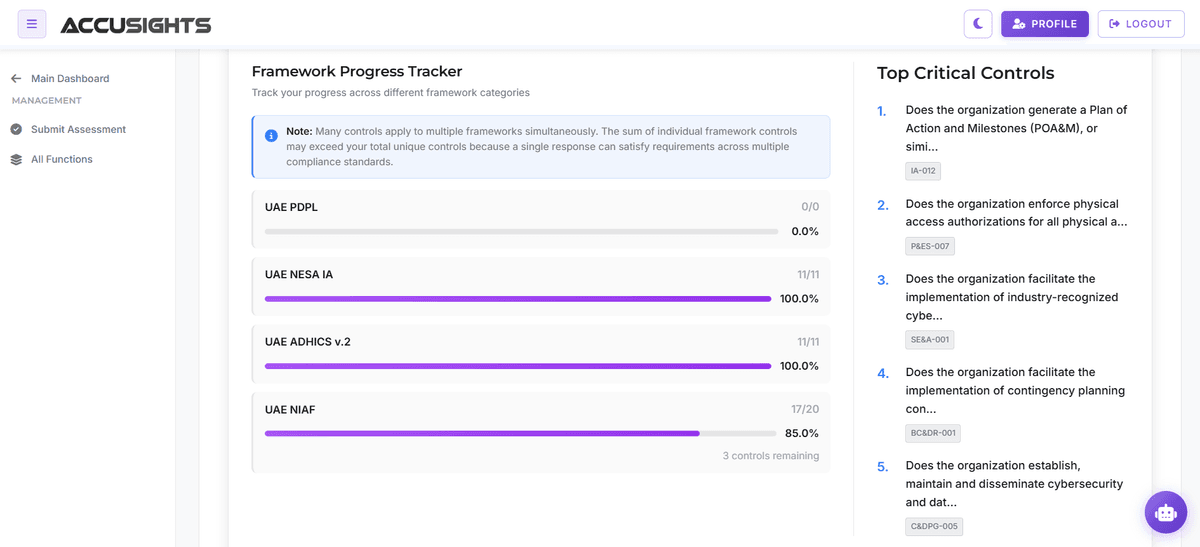
ADHICS mandates systematic risk management: asset identification, threat assessment, vulnerability analysis, and risk treatment. Healthcare organizations face sophisticated threats targeting patient data and clinical systems. We map the ADHICS risk requirements, assess whether your asset inventory, risk method and risk register exist and are current, assign remediation and keep the register DOH expects to see. Fixing the vulnerabilities stays with your IT team or its provider.
A current risk register, with each remediation item tracked to an owner.
Implement Access Control and Data Protection
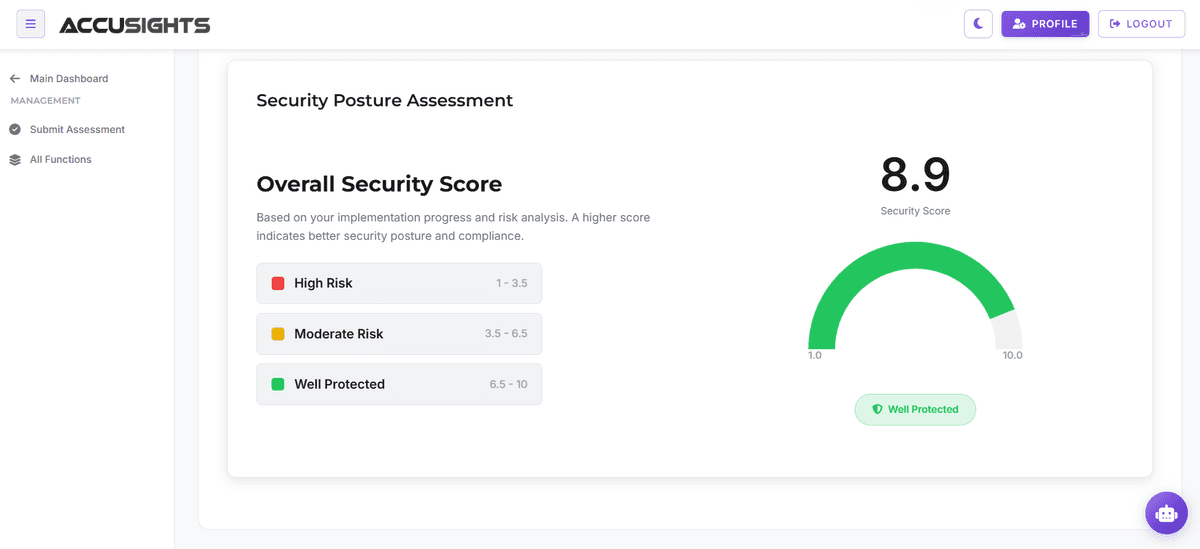
ADHICS requires strict access controls: user authentication, authorization management, privileged access controls, and data encryption. Healthcare data is highly sensitive and attractive to attackers. Access control failures enable insider threats and external breaches. AccuSights maps the ADHICS access-control requirements, validates through read-only telemetry whether multi-factor authentication, privilege assignment and encryption are configured on supported platforms, and keeps the evidence DOH reviews during security audits. The settings themselves are changed by your own administrators.
We map the access requirements, check the settings read-only and keep the evidence.
Establish Incident Response and Recovery
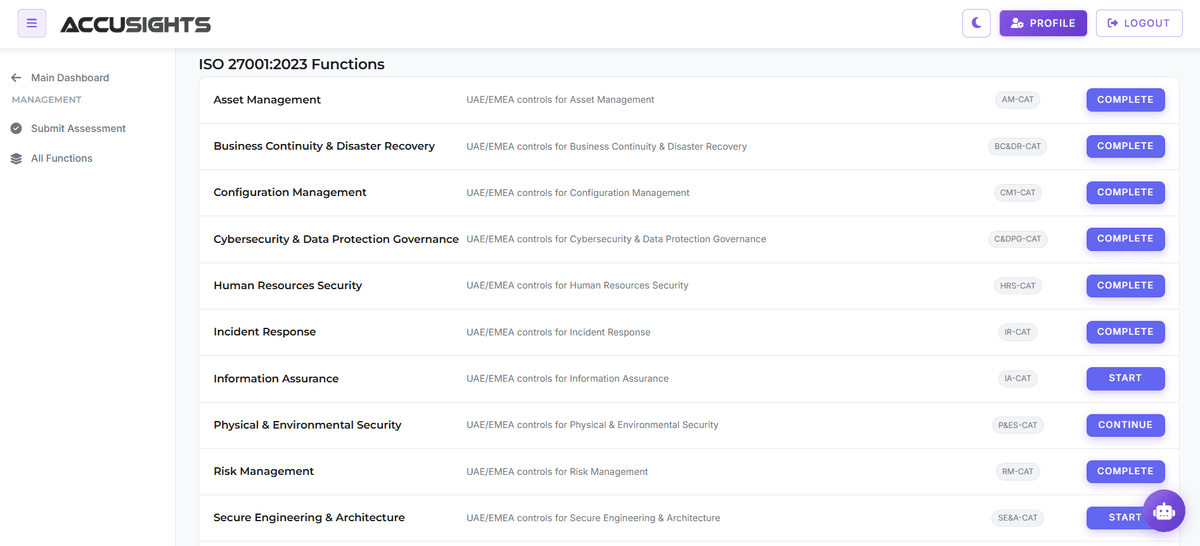
ADHICS mandates incident response capabilities: detection, analysis, containment, eradication, recovery, and lessons learned. Healthcare breaches require immediate response to protect patients and comply with notification requirements. We map the ADHICS incident requirements, assess whether your response plan, roles and 24-hour notice to DOH are in place, and keep the incident records DOH examines. Responding to an incident is done by your team or a UAE-licensed partner.
A response plan with named roles and the 24-hour DOH notice written in.
Maintain Business Continuity and Disaster Recovery
ADHICS requires business continuity planning: impact analysis, recovery strategies, backup procedures, and testing. Healthcare cannot tolerate extended downtime, patient care depends on system availability. We map the continuity requirements, assess whether your impact analysis, backup procedures and test records exist, and keep the continuity documentation DOH asks for. Running backups and recovery tests stays with your IT team.
Continuity plans and backup test records, current for the next audit.
Prepare for DOH ADHICS Audits
DOH conducts regular ADHICS compliance audits examining the domains and controls that apply to your entity type and tier, out of 692 controls across 11 domains. Audits assess governance, technical controls, documentation, and evidence of implementation. We keep the mapping, the assessment and the evidence in one place, so a DOH audit becomes a file hand-over rather than a scramble.
Evidence kept current for every control that applies to your tier.
Why Healthcare Entities Choose This Path
From the first gap assessment to evidence ready for a DOH audit.
Healthcare facilities using our platform:
Walk Into DOH Audits Ready
Requirements mapped, implementation assessed and evidence in one place, so a DOH ADHICS audit becomes a file hand-over rather than a scramble.
Protect Patient Data
The controls ADHICS sets for health information, mapped to your systems, with each gap assigned to an owner.
Document Governance
Policies, roles and oversight written down and owned, so an auditor can see who is responsible for what.
Manage Cyber Risks
Systematic risk management identifies vulnerabilities, prioritizes remediation, and reduces exposure to healthcare-targeted attacks.
Respond to Incidents
A written response plan with named roles and the 24-hour DOH notice, ready before an incident happens.
Maintain Operations
Continuity and backup plans documented and tested by your team, with the test records kept for the audit.
Built for Abu Dhabi healthcare cybersecurity and ADHICS readiness.
The 11 ADHICS Control Domains
ADHICS v2 contains 692 controls, 162 primary and 530 secondary, across 11 domains. Applicability and implementation expectations vary by entity type and control category. The platform maps ADHICS requirements, assesses implementation, manages evidence and remediation, and validates selected technical controls through supported telemetry.
The standard runs from workforce security and asset management through access, operations, communications, health information, third parties, systems development, incident management and continuity. Which controls apply to you, and to what depth, depends on your entity type and your tier: Basic, Transitional or Advanced. We confirm your tier first, map your existing controls to the domains that apply, and keep the evidence in one place for licence renewal.
692 controls across 11 domains, each one mapped, assessed and backed by evidence.
ADHICS Security Domains
Healthcare cybersecurity across every domain