
The Dubai free zone
DIFC Data Protection Law, in plain terms
Every company operating in the Dubai International Financial Centre answers to the DIFC Data Protection Law for the personal data it holds, with the Commissioner of Data Protection as its regulator. We map those obligations to one control set and keep the evidence ready for the Commissioner.
Get ready for your DIFC data protection review
The records, controls and evidence the Commissioner can ask for
DIFC has its own data protection law and its own regulator.
The Dubai International Financial Centre is a distinct legal jurisdiction with its own Data Protection Law, modeled on GDPR but adapted for Dubai's financial services ecosystem. The DIFC Commissioner of Data Protection oversees the law, and under Article 41 a controller must notify the Commissioner of a qualifying breach as soon as practicable.
One control set for the DIFC data protection obligations that apply to you.
Map Every Data Flow and Processing Activity
DIFC Law requires you to know exactly what personal data you process, where it comes from, where it goes, and why you're processing it. The Commissioner expects complete data mapping during audits. AccuSights structures that work: it records the processing activities you identify, documents the legal basis for each and keeps the Records of Processing Activities (ROPA) in the form the Commissioner expects. Finding the data across your systems is done with your teams, not discovered for you.
Processing activities recorded with a legal basis for each, in a ROPA kept current.
Map the Required Data Protection Controls
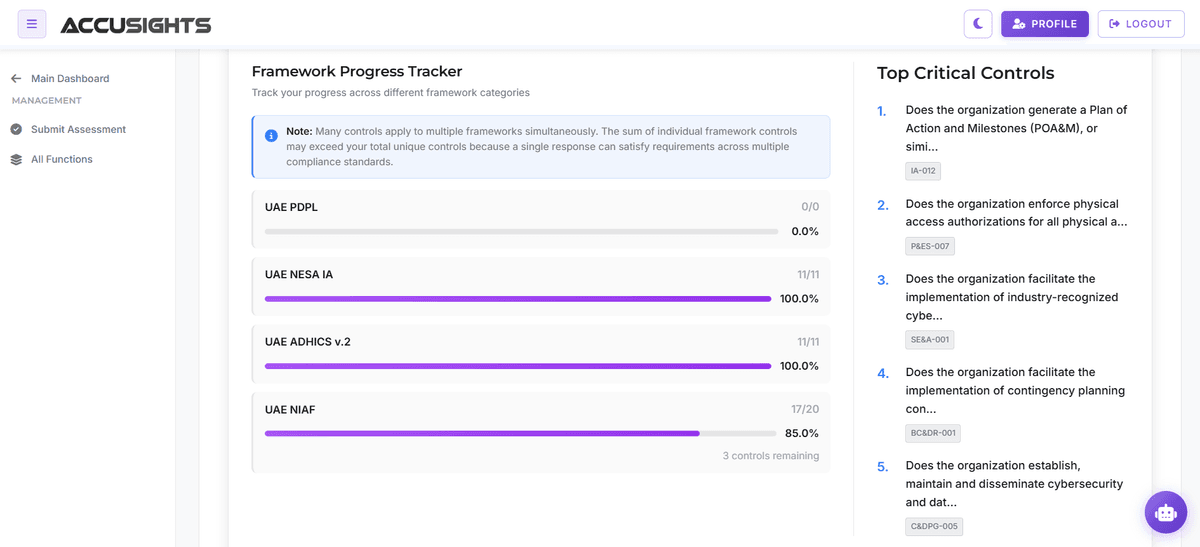
DIFC Law mandates specific controls: consent management, data minimization, access controls, encryption, data retention limits, and more. We map those controls to your systems, assess whether each one exists, assign remediation and keep the evidence the Commissioner can ask for. Your own teams configure the controls.
Each required control mapped, assessed and backed by evidence.
Notify the Commissioner as Soon as Practicable
Article 41 of the DIFC Data Protection Law requires a controller to notify the Commissioner as soon as practicable when a personal-data breach compromises an individual's confidentiality, security or privacy. Notification to affected individuals may also be required where the breach presents a high risk. AccuSights holds the breach-response procedure, records the assessment behind each decision and keeps the notification evidence the Commissioner asks for. Judging the breach and sending the notification stay with the controller.
We map the Article 41 duty, assess the procedure and keep the notification evidence.
Appoint a Data Protection Officer (If Required)
DIFC Law requires certain organizations to appoint a Data Protection Officer, someone with expertise, independence, and adequate resources. Whether the DPO is on staff or external, we give them the mapped obligations, the records and the evidence they need to do the job. Appointing the DPO stays with you.
The records and evidence your DPO needs, in one place.
Handle Data Subject Rights Requests Properly
DIFC Law grants data subjects rights to access, rectify, erase, and restrict processing of their data. You must respond within strict timelines. AccuSights holds the rights-request procedure, tracks the deadline on each request and keeps the record of what was decided and sent. Verifying the requester and answering them stays with your team.
A documented procedure, with the deadline and outcome of each request recorded.
Prepare for Commissioner Investigations and Audits
The DIFC Commissioner has broad powers to investigate, audit, and enforce. When they arrive, they expect immediate access to policies, ROPA, breach records, consent documentation, and evidence of controls. We keep that documentation current and in one place, so a request from the Commissioner is answered from records you already hold.
The documents the Commissioner asks for, current and in one place.
Why DIFC Companies Choose This Approach
From the first gap assessment to records ready for the Commissioner.
Companies using our platform:
Records the Commissioner Can Check
ROPA, legal bases, impact assessments and processor agreements kept current, so the Commissioner can check each one.
An Owner for Every Obligation
Each obligation in the law has a named owner and a remediation date, so gaps do not sit unassigned.
Ready for the Commissioner
Each control has an owner and current evidence, so a request from the Commissioner for proof gets a document the same day.
Meet the Article 41 Notification Duty
A documented breach-response procedure and a kept assessment record mean you can notify the Commissioner as soon as practicable, which is what Article 41 actually requires.
Handle Rights Requests Properly
A documented rights-request procedure and tracked deadlines, so each request has a due date and a record.
Build Client Trust
Records you can show a client who asks how their data is handled.
Built for DIFC data protection readiness and continuous compliance management.
What the DIFC Data Protection Law asks of you
The law is detailed. We map it, assess it and keep the record; we do not run it.
The DIFC Data Protection Law imposes obligations on controllers and processors, grants rights to data subjects, and empowers the Commissioner to investigate and enforce. Each requirement has specific documentation and implementation expectations. We map the obligations that apply to you, assess whether the policies and controls exist, assign remediation and keep the supporting evidence for Commissioner oversight.
We map the obligations, assess what is in place and keep the evidence.
DIFC Data Protection Requirements
What the law requires of controllers and processors