
The federal cybersecurity authority
What UAE Cyber Security Council guidance asks of your organization
Government entities and critical infrastructure operators in the UAE work to Cyber Security Council guidance, and entities designated under the Information Assurance Regulation self-assess and report against it. We map those requirements to one control set and keep the evidence ready for your next review.
Get ready for your UAE CSC review
The controls, evidence and self-assessment records behind your program
UAE CSC protects the nation's digital infrastructure.
The UAE Cyber Security Council is the national authority for cybersecurity strategy and standards. UAE CSC sets mandatory cybersecurity controls for all federal government entities, local government agencies, and critical infrastructure operators across energy, telecommunications, finance, transportation, healthcare, and water sectors. The Council publishes national guidance and advisories, coordinates incident response, and runs NCAP, a programme approved by Cabinet in February 2025 whose deadlines and phases are not yet public.
One control set for the Council requirements that apply to your organization.
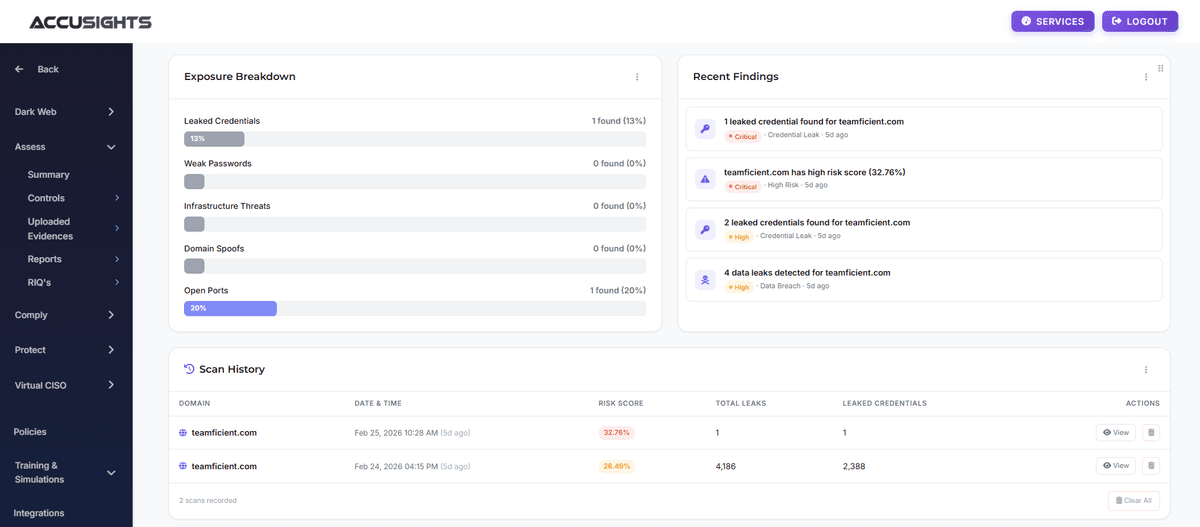
Establish Cybersecurity Governance Framework
UAE CSC requires formal cybersecurity governance: policies, procedures, organizational structure, roles and responsibilities, and oversight mechanisms. We map the governance requirements, assess whether your policies, structure and roles exist, assign remediation and keep the governance documentation a reviewer asks for. Approving policies and naming roles stay with your entity.
Governance requirements mapped, with an owner for each policy and role.
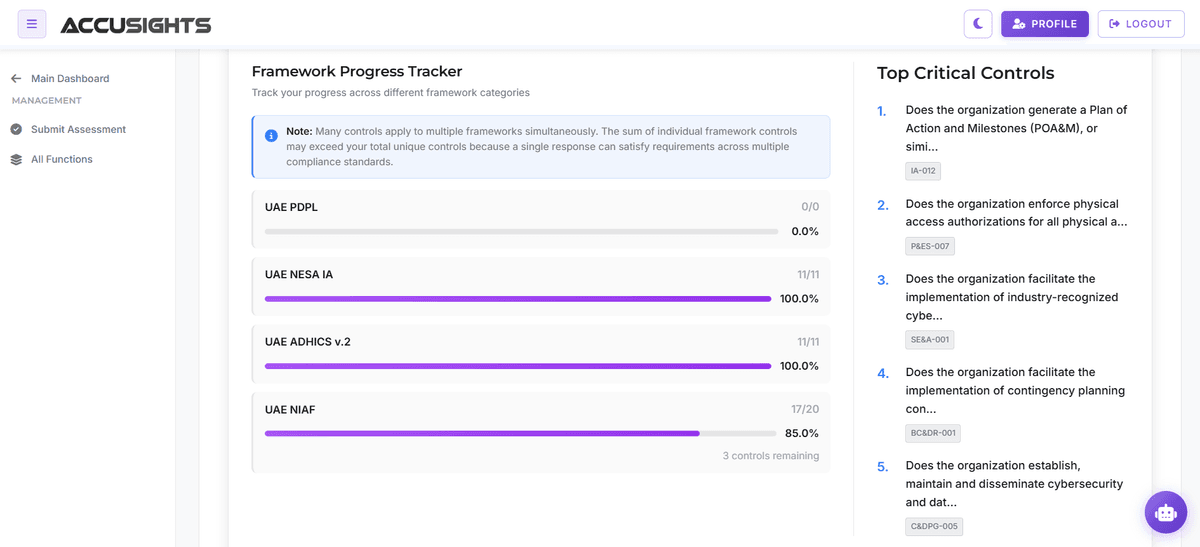
Implement Risk Management Programs
UAE CSC mandates systematic risk management: asset identification, threat assessment, vulnerability analysis, risk evaluation, and treatment planning. Critical infrastructure faces sophisticated nation-state threats and advanced persistent threats. We map the risk requirements, assess whether your asset inventory, risk method and risk register exist and are current, assign remediation and keep the risk documentation. Fixing the vulnerabilities stays with your IT team or its provider.
A current risk register, with each remediation item tracked to an owner.
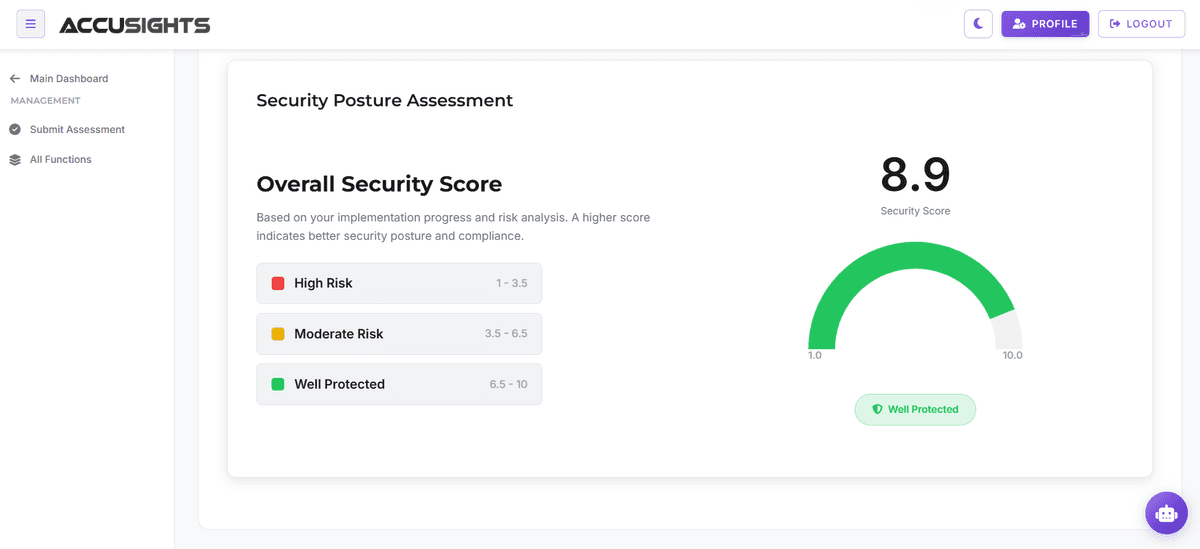
Implement Access Control and Identity Management
UAE CSC requires strict access controls: user authentication, authorization management, privileged access controls, multi-factor authentication, and access monitoring. Critical infrastructure systems are high-value targets. We map the access requirements, check read-only on supported platforms whether multi-factor authentication and privilege assignment are configured, and keep the evidence. Your own administrators change the settings.
We map the access requirements, check the settings read-only and keep the evidence.
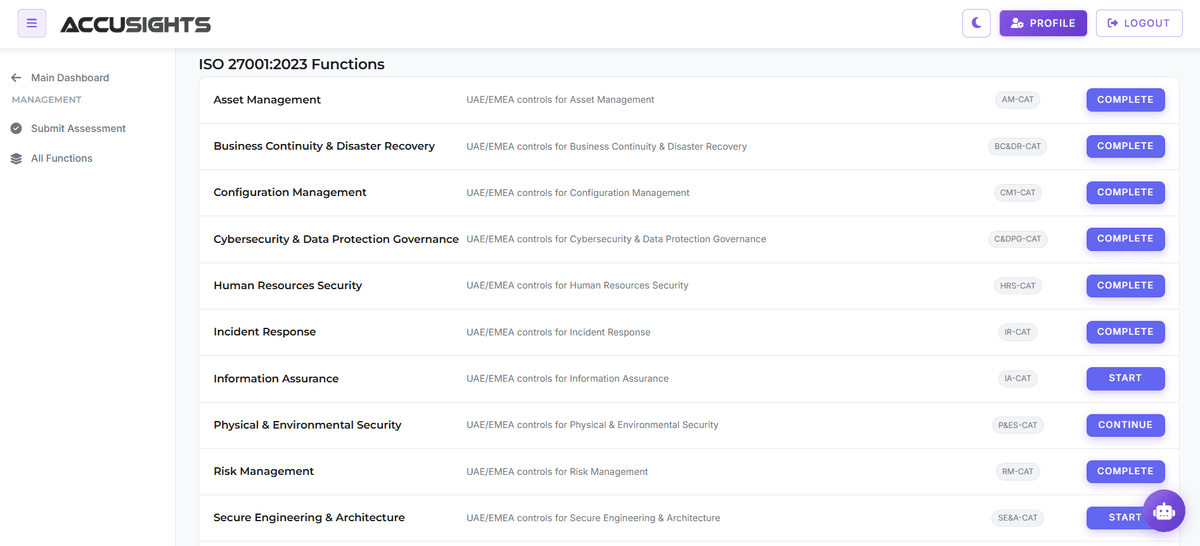
Establish National Incident Response Capabilities
UAE CSC mandates incident response capabilities: detection, analysis, containment, eradication, recovery, and coordination with national authorities. Critical infrastructure incidents require immediate reporting to UAE CSC and coordinated national response. AccuSights maps the incident-response requirements, assesses whether the detection, containment and recovery procedures exist, and keeps the incident records compliance requires. Reporting to and coordinating with the UAE CSC is done by the entity.
We map the response requirements, assess the procedures and keep the incident records.
Maintain Business Continuity for Critical Services
UAE CSC requires business continuity planning: impact analysis, recovery strategies, backup procedures, and regular testing. Critical infrastructure must maintain operations during cybersecurity incidents, national security and public safety depend on continuous service. We map the continuity requirements, assess whether your impact analysis, backup procedures and test records exist, and keep the continuity documentation. Running backups and recovery tests stays with your IT team.
Continuity plans and backup test records, kept current.
Prepare for Self-Assessment and Review
Entities designated under the UAE Information Assurance Regulation self-assess and report at the level their designation requires. The Council also runs NCAP, a programme approved by Cabinet in February 2025 whose deadlines, phases and assessors are not yet public. We keep the mapping, the assessment and the evidence in one place, so a self-assessment or a later review starts from a current file rather than a scramble.
Evidence kept current for the controls that apply to your designation.
Why Critical Infrastructure Operators Choose This Path
From the first gap assessment to evidence ready for review.
Organizations using our platform:
Ready for Review
Each control has an owner and current evidence, so a self-assessment or a reviewer asking for proof gets a document the same day.
Protect Critical Infrastructure
National cybersecurity controls protect essential services from sophisticated threats, safeguarding public safety and economic stability.
Document Governance
Policies, roles and oversight written down and owned, so a reviewer can see who is responsible for what.
Manage National Risks
Systematic risk management identifies threats to critical infrastructure, prioritizes remediation, and reduces national security exposure.
Coordinate Incident Response
Incident-response requirements mapped, procedures assessed and records kept. Reporting to and coordinating with the UAE CSC stays with your team.
Maintain Operations
Continuity and backup plans documented and tested by your team, with the test records kept for review.
Built for Cyber Security Council readiness and continuous national-infrastructure compliance management.
The security control areas the UAE CSC sets
The UAE Cyber Security Council sets security controls across its domains, and which of them apply depends on your sector and classification. The platform maps the requirements, assesses implementation, manages evidence and remediation, and validates selected technical controls through supported telemetry.
UAE CSC sets cybersecurity requirements across governance, risk management, asset management, access control, cryptography, physical security, operations security, communications security, system acquisition, supplier relationships, incident management, business continuity, and compliance. We map the requirements that apply to you, assess whether the controls exist, assign remediation and keep the evidence. Running the controls stays with your team.
The control areas, and which of them we map.
UAE CSC Control Domains
Which controls apply depends on your sector and classification